VISITOR MANAGEMENT SYSTEM
5 Questions Your Auditor Will Ask About Visitor Management
Visitor management doesn't usually top the list when preparing for an ISO audit.
It should - because it's one of the easiest places to be caught with a process that looks fine on the surface and falls apart under a real question.
350+ Enterprise customers across all products


Question 1
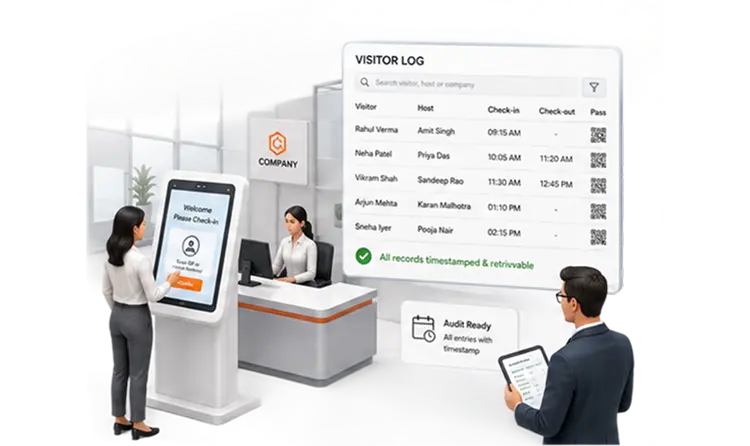
Can You Show Who Registered, And When?
A manual register - often barely legible - isn't a record an auditor accepts. They expect a timestamped, retrievable log as proof, not handwriting someone has to interpret.
Question 2
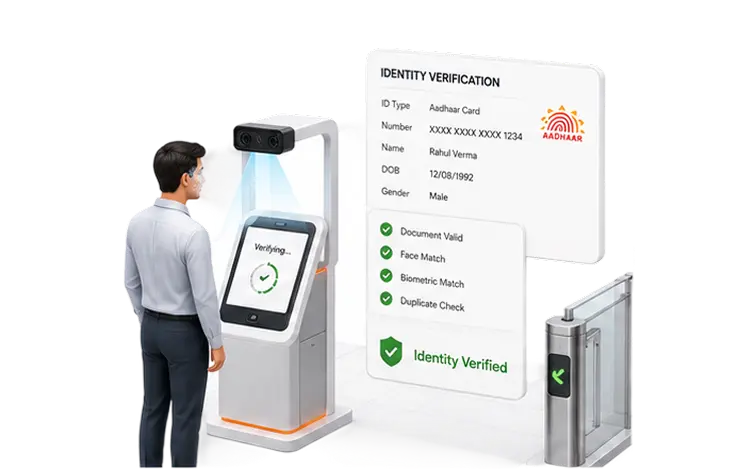
Was That Visitor's Entry Actually Verified?
A photo of an ID isn't verification, and fake IDs are more common than most facilities assume. Auditors want to see that identity was cross-referenced, not just collected.
Question 3
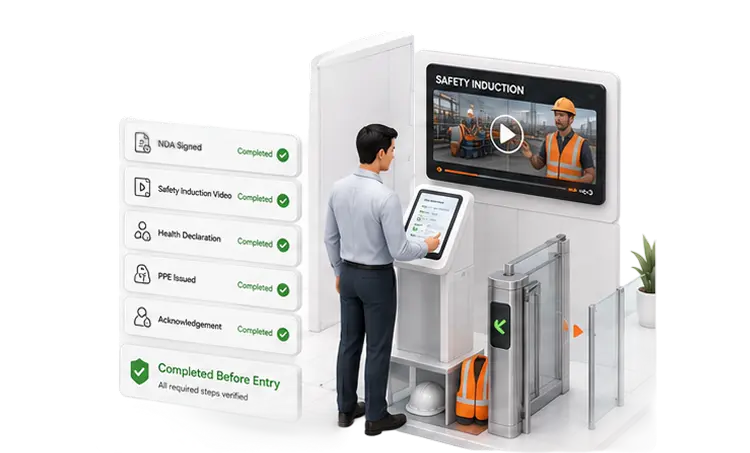
Were Safety And Compliance Steps Completed Before Entry, Not After - With Proof?
NDAs, safety video inductions, health declarations, PPE issuance - if your standard procedure requires them, can you prove they actually happened, not just that they're policy? In factories especially, an unproven safety induction is a real accident risk, not just a paperwork gap.
Question 4
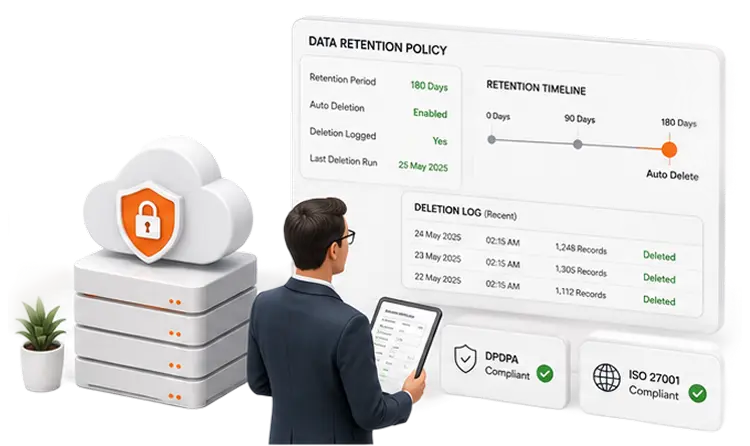
What's Your Retention Policy, And Can You Defend It?
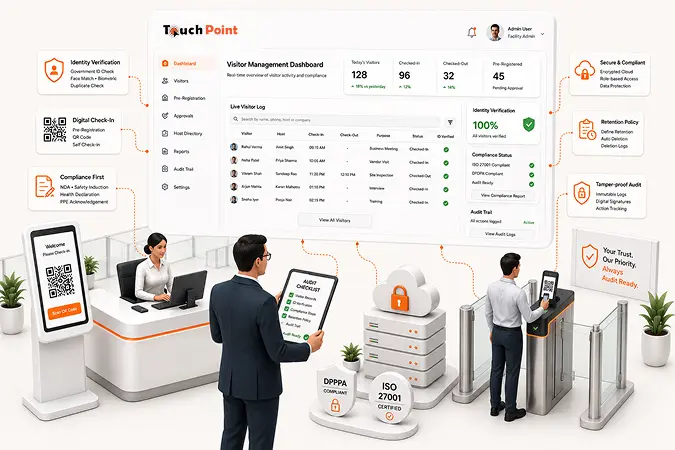
With DPDPA enforcement underway, "we keep everything" or "we're not sure" isn't an answer an auditor will accept. They'll ask how long visitor data is retained and how it's deleted.
Question 5
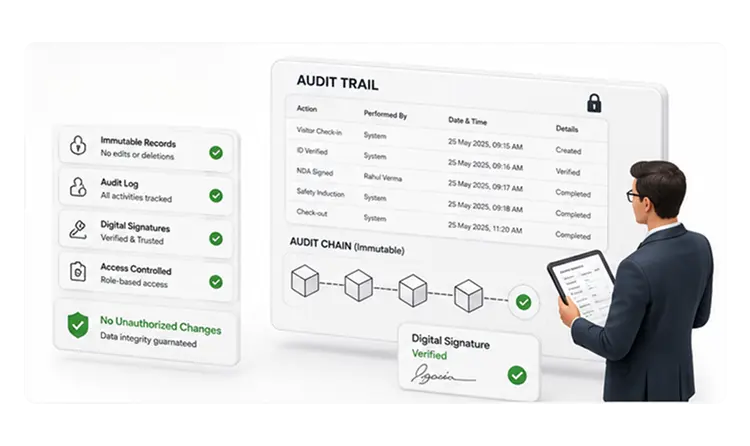
Is Your Visitor Log Tamper-Proof?
Anyone can produce a record after the fact. Auditors ask whether that record can be edited or deleted without a trace - whether there's an audit log proving the data hasn't been manipulated.